gets past MFA
Browser-in-the-Middle
Real time session hijacking through headless Chrome. It proxies the genuine login page and captures MFA tokens, cookies, localStorage, and the browser profile.
Train your team against the attacks they actually face
100%
64%
22%
8%
22%
Every stage leaves an auditable trace, so the simulation result does not stop at a click count.
Target groups, schedule, and rules of engagement are agreed up front.
Templates and channels are chosen, and every recipient gets a unique link of their own.
Opens, clicks, replies, and QR scans are all recorded with their timestamps.
The credential page records the attempt without ever storing the real password.
Whoever fails is enrolled straight into the relevant course, automatically.
Risk scores per department and a summary ready for the board meeting.
An HTML template with a tracking pixel, reply tracking, and a beaconed attachment. Every recipient gets a unique link, so interaction can be mapped person by person.
Your parcel is being held at the depot. Confirm your address within 24 hours: bit.ly/kirim-ulang
Delivery runs through Twilio and WAHA with tracking URLs, so delivery status and engagement are visible in the same detail as the email channel.
QR codes with an embedded tracking URL, made for tests in physical spaces such as car park posters, the reception desk, or event invitations.
Not just a fake link. This set tests how ready the team is against techniques attackers already use in the field.
Real time session hijacking through headless Chrome. It proxies the genuine login page and captures MFA tokens, cookies, localStorage, and the browser profile.
A fake CAPTCHA page or system prompt that walks the target into running a PowerShell command. Cloudflare, reCAPTCHA, and Windows Update templates are included.
An OAuth phishing simulation: the user logs in normally, then is asked to copy a URL containing the authorization code into a malicious page.
An OAuth 2.0 Device Authorization Grant simulation against Microsoft Entra ID, with token capture and reconnaissance through the Microsoft Graph API.
A transparent MITM proxy for advanced simulations. Each phishlet defines its proxy hosts, credential capture rules, and bait URLs.
Scope, time window, and forbidden actions are agreed before the campaign starts, complete with an emergency stop procedure.
Learning paths arrange the curriculum in order with prerequisites, guiding a participant from the basics through to advanced material.
Upload, edit, and serve SCORM packages with progress tracking, exam scoring, and certificates.
Turn any PDF into an interactive course with AI generated modules and quizzes.
A tiered curriculum with prerequisites between modules.
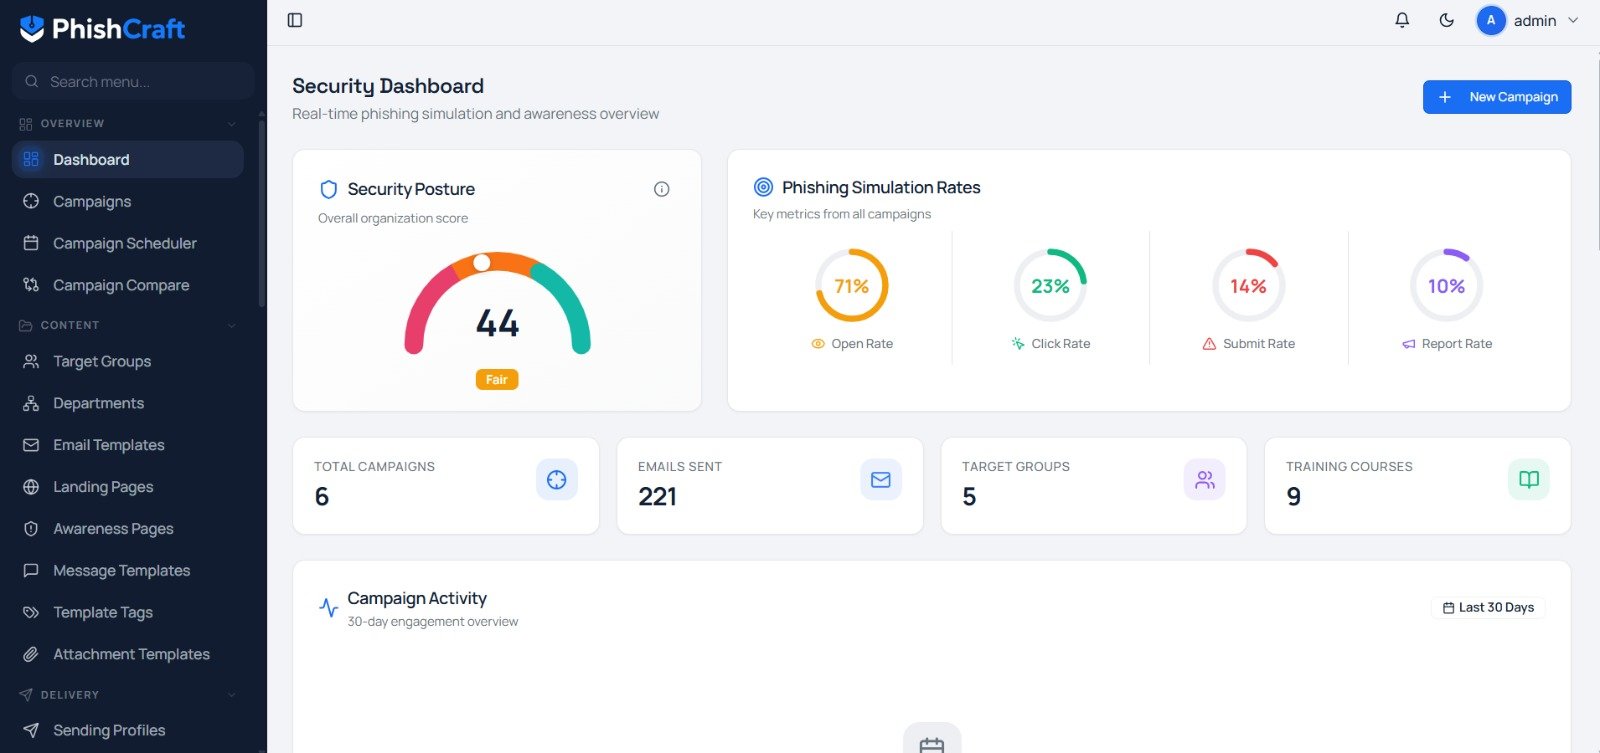
A real time posture gauge, phishing funnel, activity chart, and a live event feed in one dashboard.
Financial impact estimates, annualized loss expectancy, and high risk user identification all follow the same numbers.
A board ready overview with AI insight, industry benchmarks, and export formats.
Open rate, click rate, and submission rate side by side across campaigns.
A multi platform extension with browser level monitoring, giving real time protection against phishing, session hijacking, identity abuse, and tracking.
Granular permissions are enforced on both the frontend and the backend, and multi tenant isolation makes sure data never crosses a workspace boundary.
Connect the major LLM providers through the Model Context Protocol for real time access to campaign data, template generation, and risk summaries.
We run one sample campaign together with your team, from building the bait to the risk report you can take into a meeting.