One CTI workspace
Indicators, advisories, campaigns, and attack surface findings live in one place instead of scattered across many tools.
A CTI platform that collects, correlates, and visualises threat data from many sources in one workspace. Intelligence is exchanged over STIX 2.1 and TAXII 2.1, so findings go straight to work in the SIEM, SOAR, EDR, and network gear you already own.
Intelligence modules
Stealer malware families
App platforms watched
Lookalike domain techniques
Indicators, advisories, campaigns, and attack surface findings live in one place instead of scattered across many tools.
Built-in STIX 2.1 and TAXII 2.1 support lets intelligence flow both ways with partners and other security platforms.
The AI assistant summarises reports, pulls out entities and IOCs, then maps them to MITRE ATT&CK techniques.
Exposed assets, lookalike domains, and leaked credentials are found before anyone uses them against you.
Indicators are exported to IDS, SIEM, and firewalls through feeds that stay in sync on their own.
Self-hosted deployment with Docker Compose. Data and infrastructure stay inside your own environment.
Every module stands on the same data, so a finding in one place immediately enriches the context everywhere else.
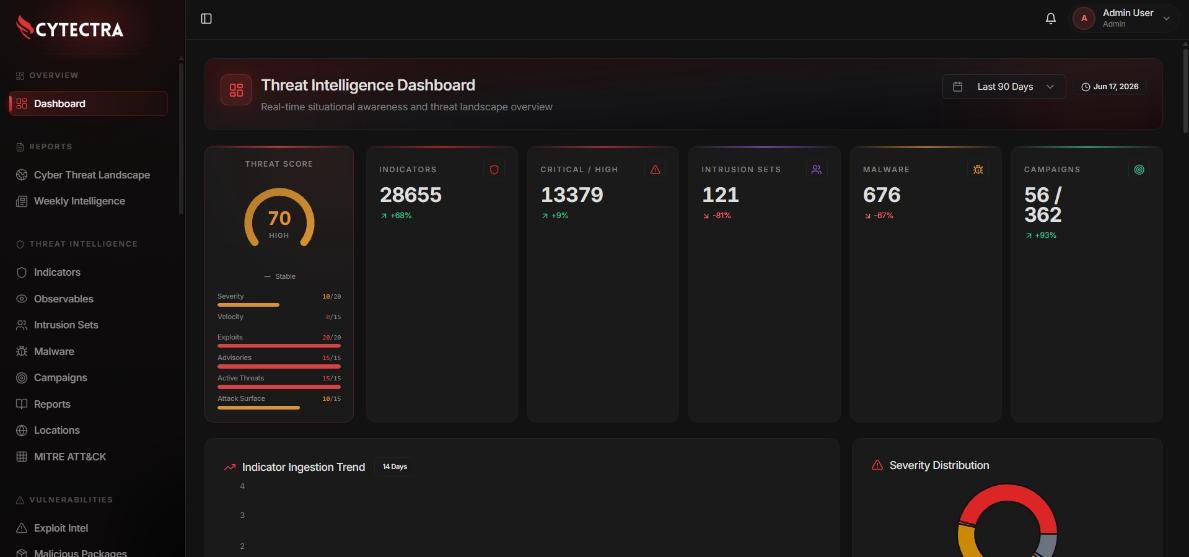
The command centre for every threat intelligence activity.
Threat score, indicator counts, critical and high priority findings, intrusion sets, malware, and campaigns all sit on one screen. Visual summaries and ranked lists help the team see what needs handling first.
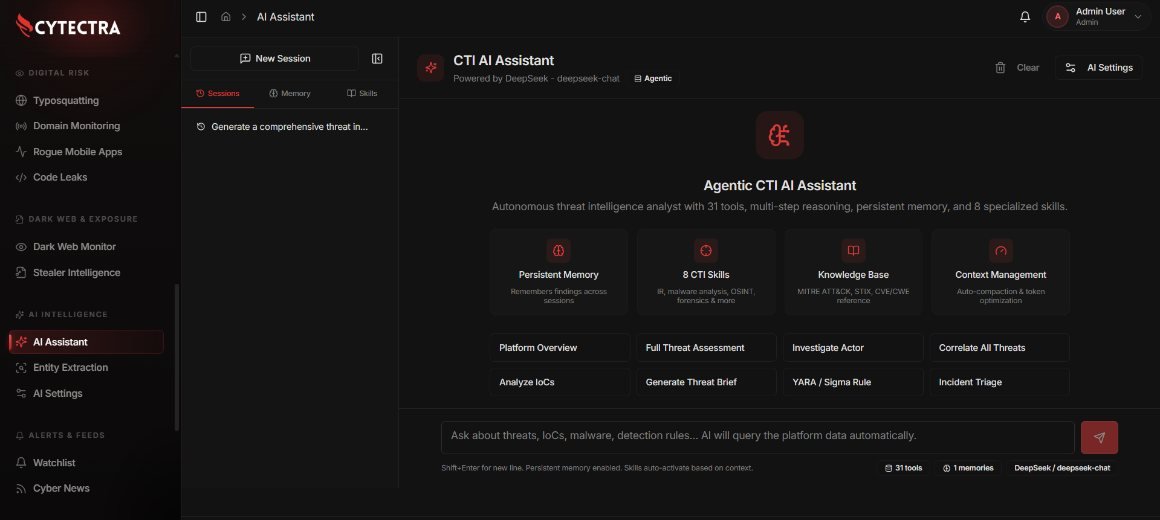
Investigation and correlation that move faster.
The AI assistant brings CTI data, MITRE ATT&CK knowledge, IOC analysis, and threat context together in one interactive workspace. It supports several AI providers and models, so the rollout can follow your internal policy.
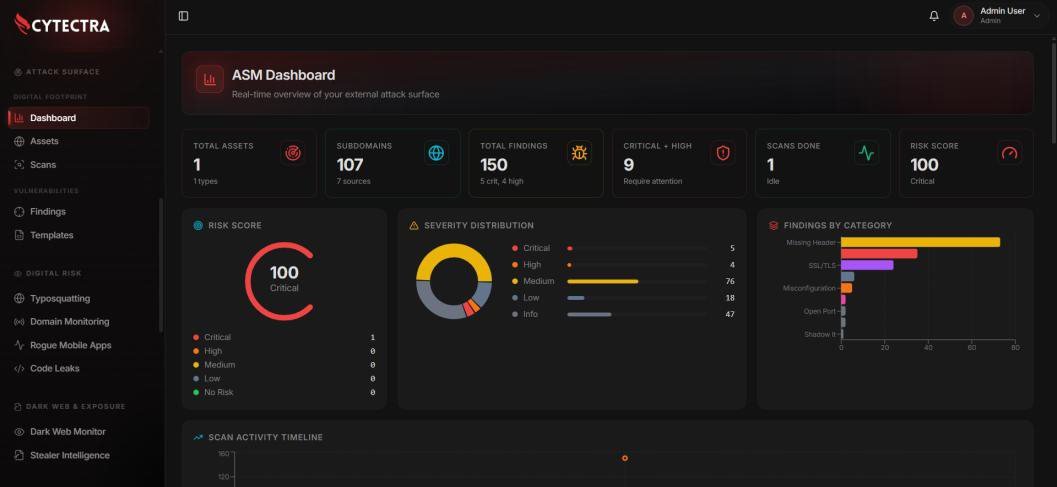
Continuous visibility over internet facing assets.
A layered scanning engine finds new assets, tests for vulnerabilities, validates exposure, then tracks remediation status over time. Smart validation keeps false positives down so the team does not burn hours chasing empty findings.
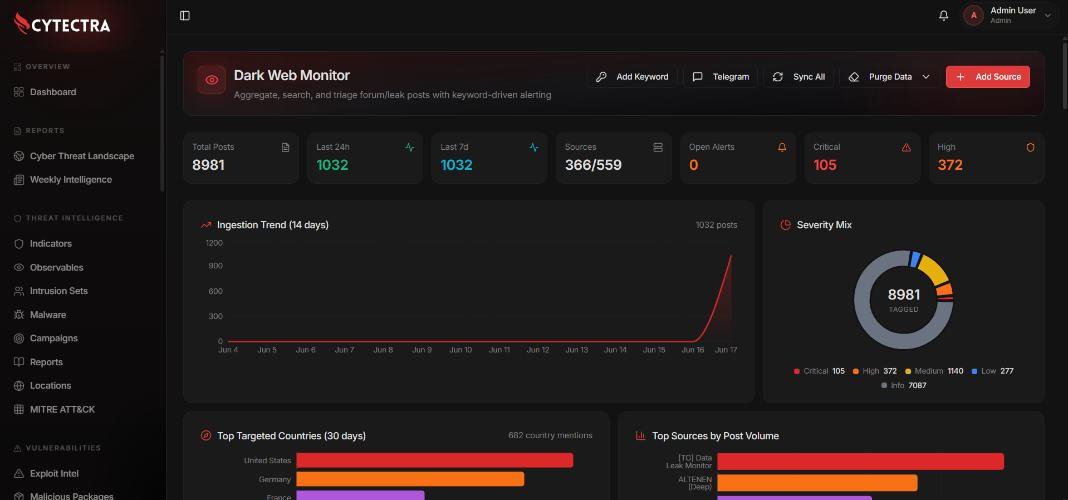
Early signals from where stolen data is traded.
Underground forums, marketplaces, leak sites, and Telegram channels are watched through one central search. AI assisted classification and false positive filtering keep the alerts relevant to your team.
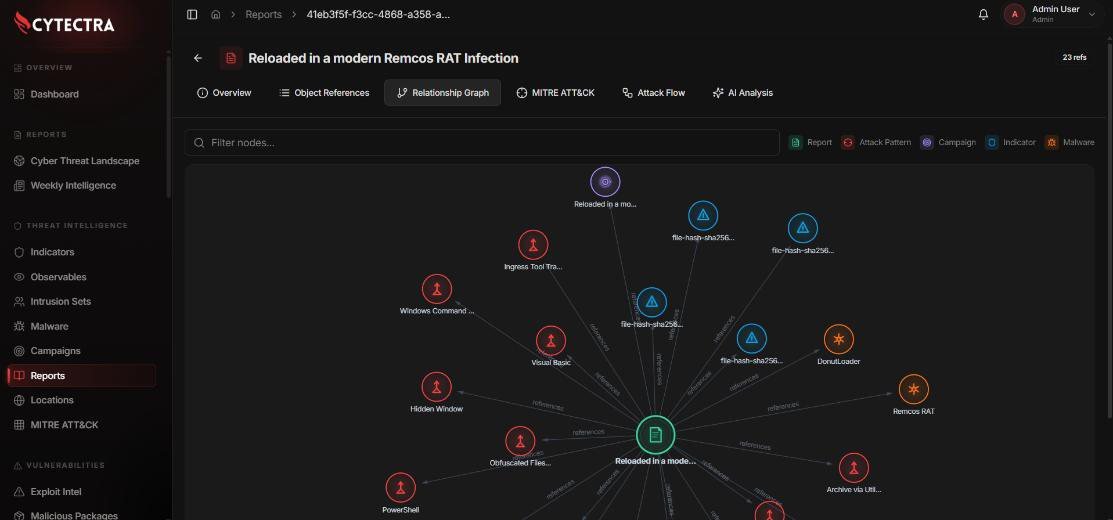
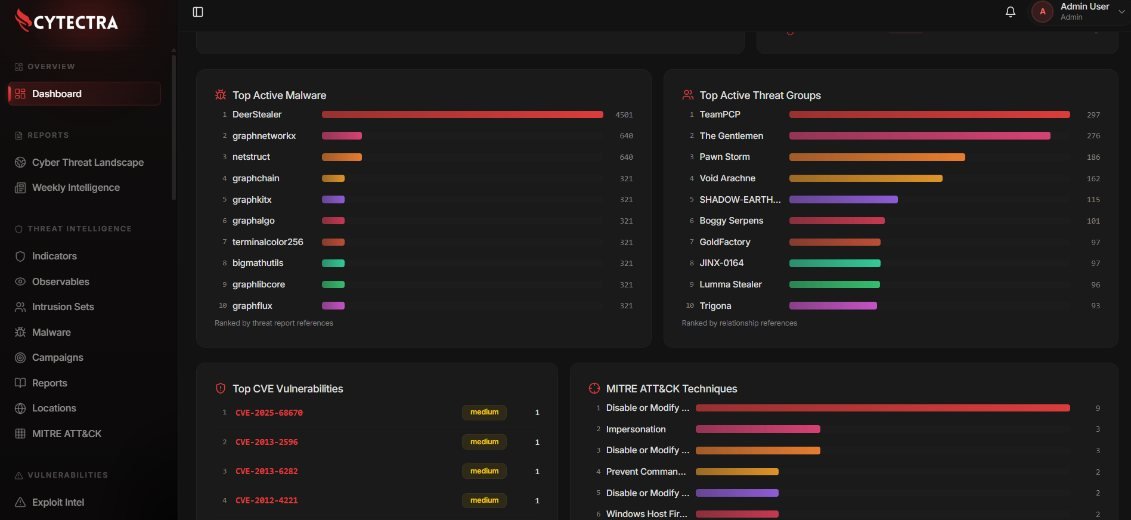
An interactive relationship graph between malware, indicators, campaigns, threat actors, and ATT&CK techniques.
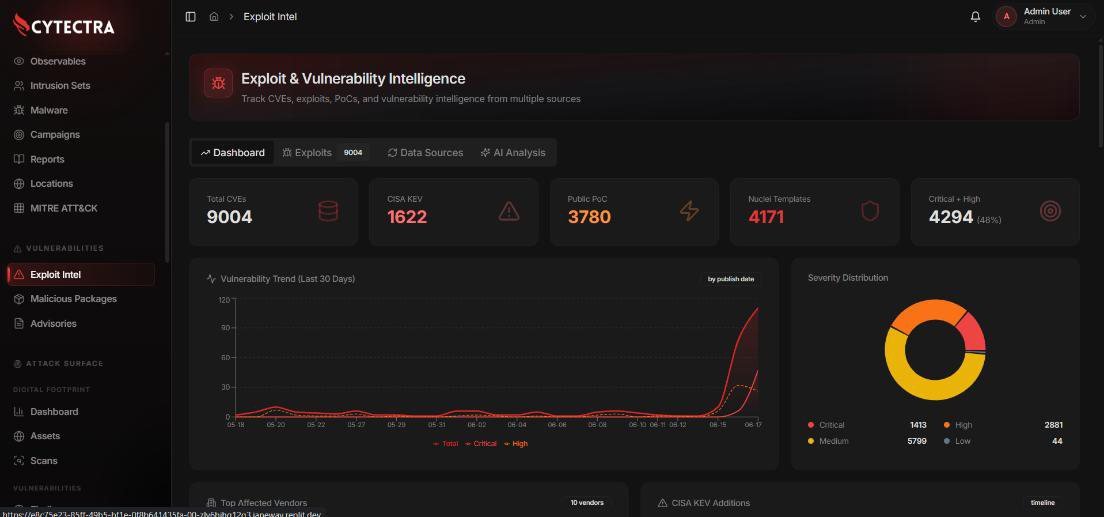
CVEs, the CISA KEV list, PoC availability, Metasploit modules, and EPSS scores for risk based prioritisation.
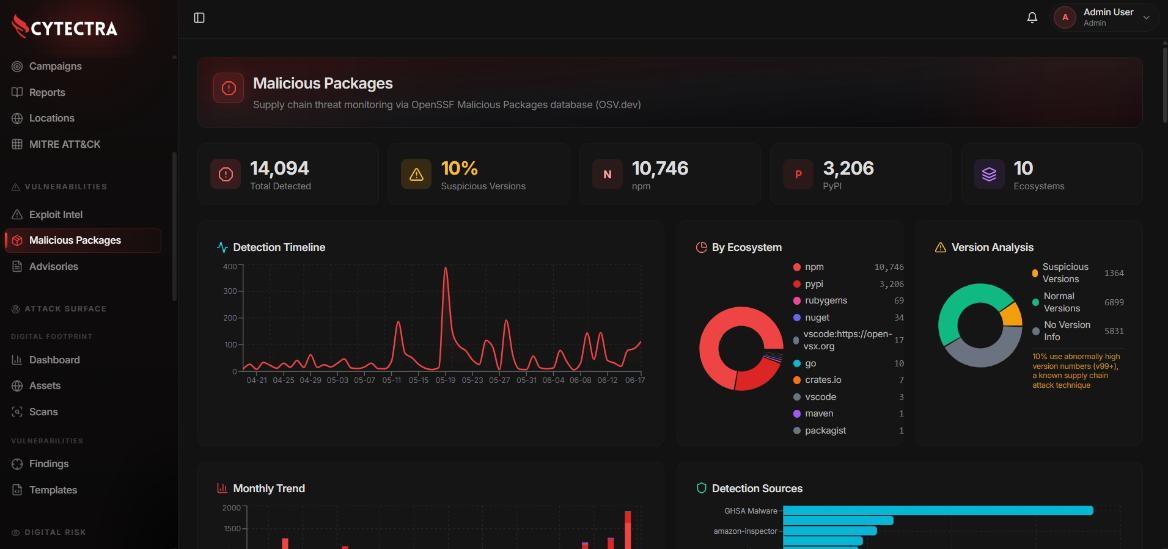
Malicious packages across npm, PyPI, RubyGems, Go, Maven, NuGet, and crates.io, sourced from the OSV database.
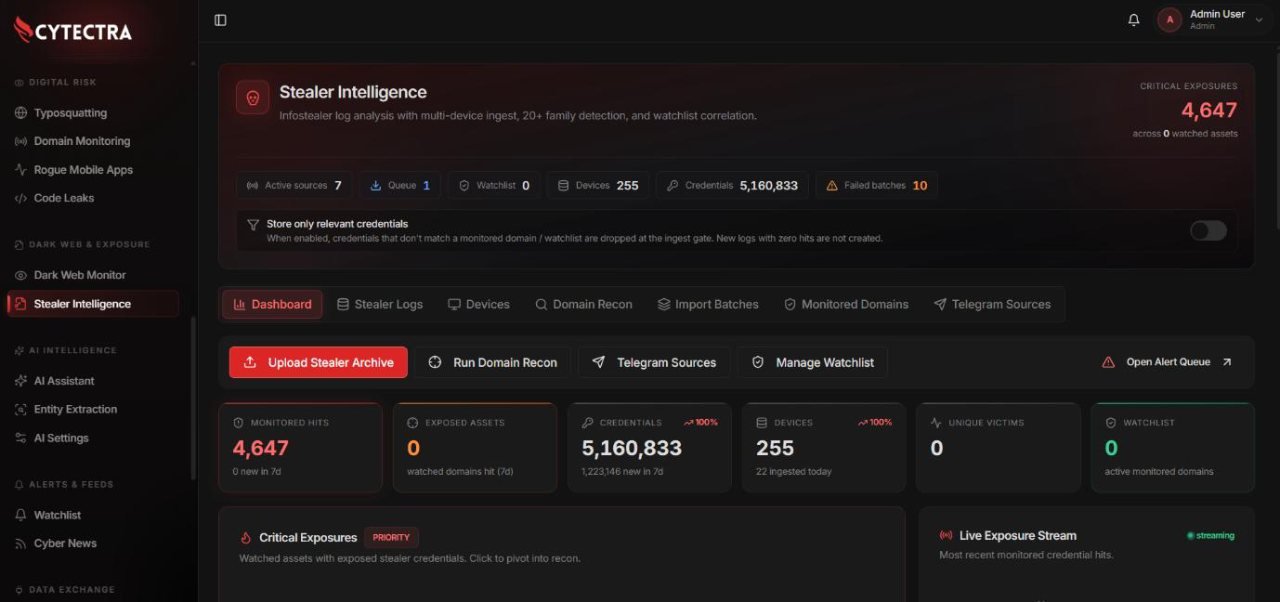
Compromised credentials, devices, and subdomains from info-stealer logs across 20 malware families.
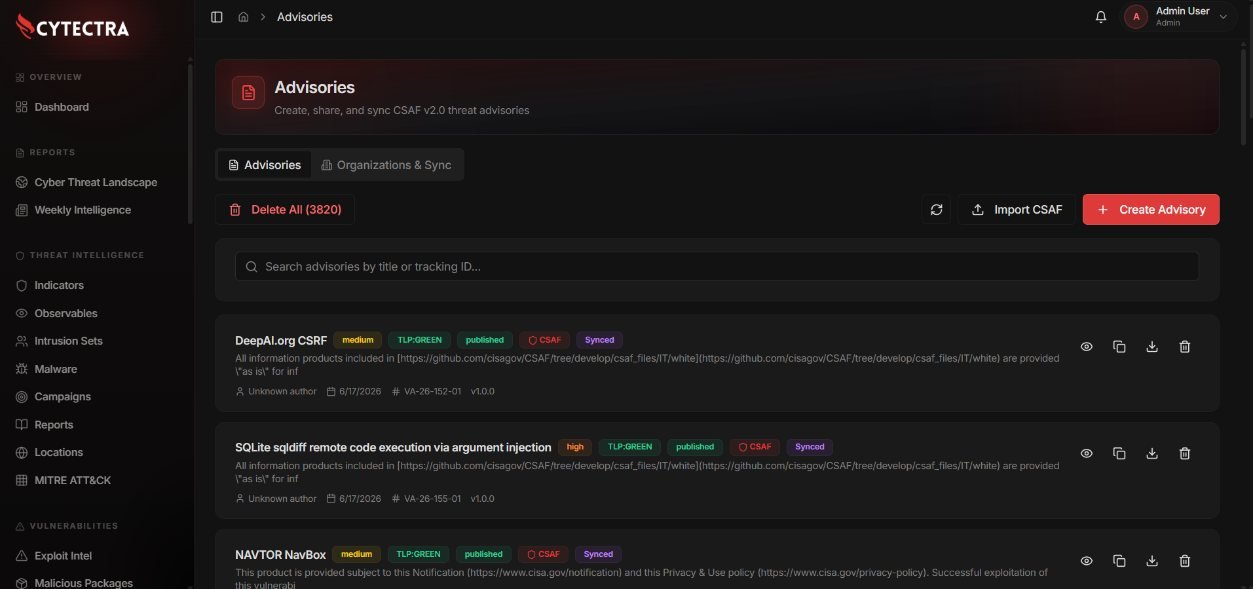
Advisory authoring, validation, publishing, and synchronisation, complete with affected asset correlation.
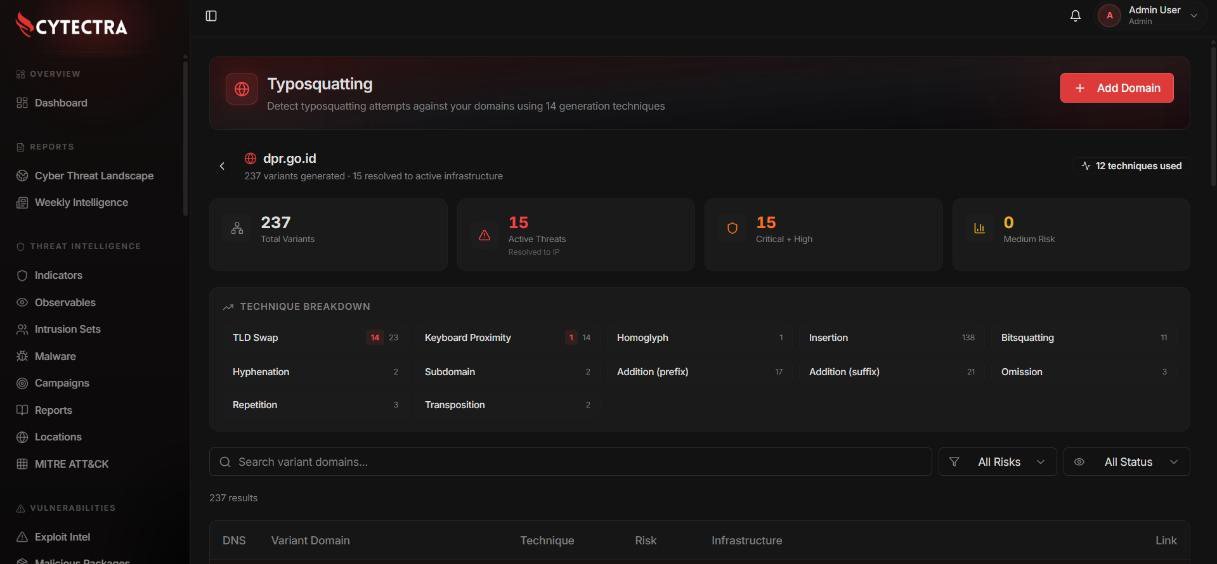
Domain variant generation with 14 techniques, DNS analysis, and similarity scoring to hunt lookalike domains.
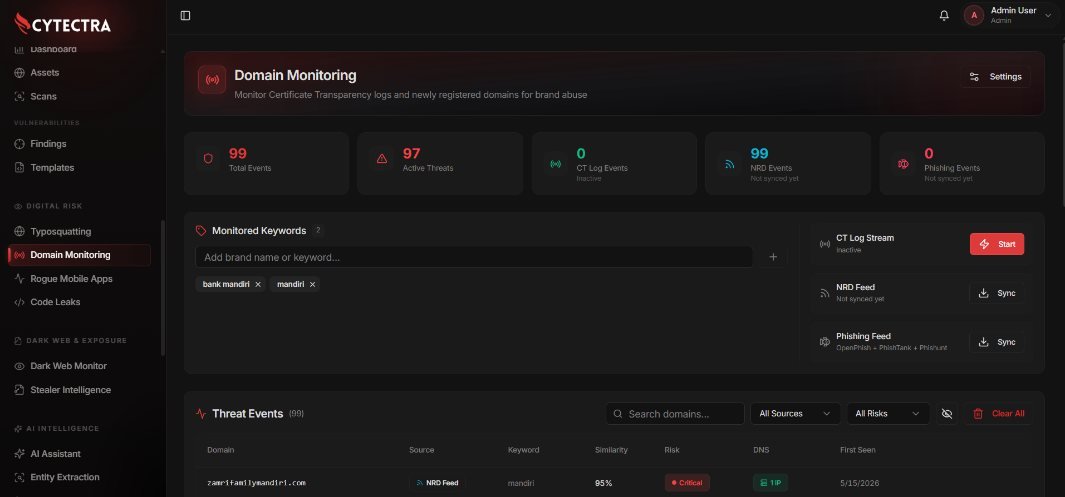
Certificate Transparency logs and newly registered domain feeds with fuzzy matching on brand keywords.
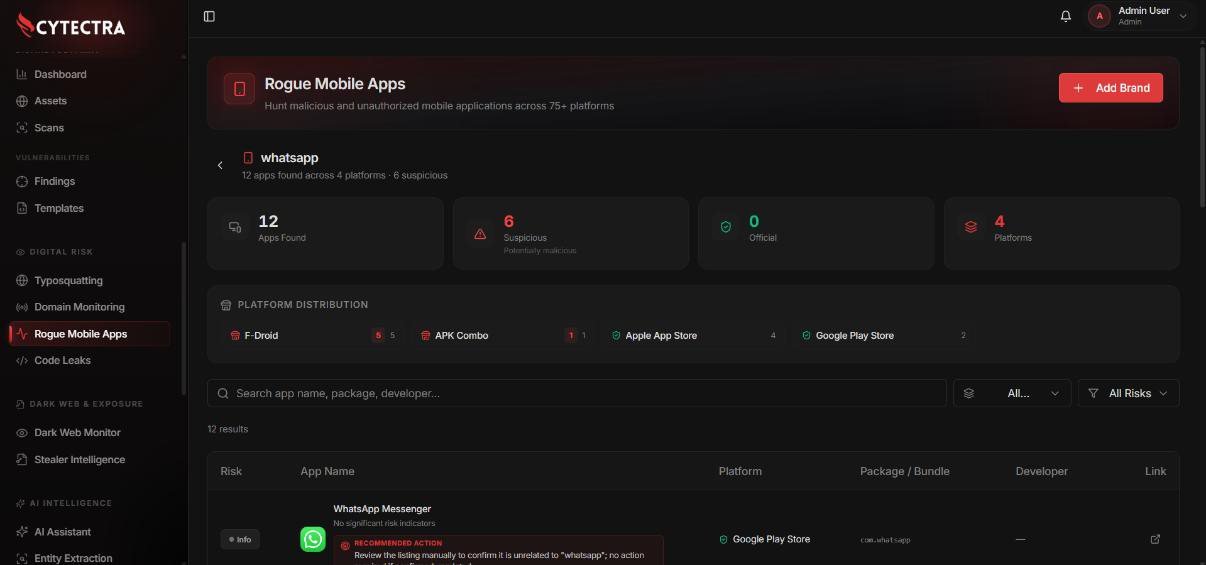
Fake and malware laden apps across more than 75 official and third party stores, each with a risk score.
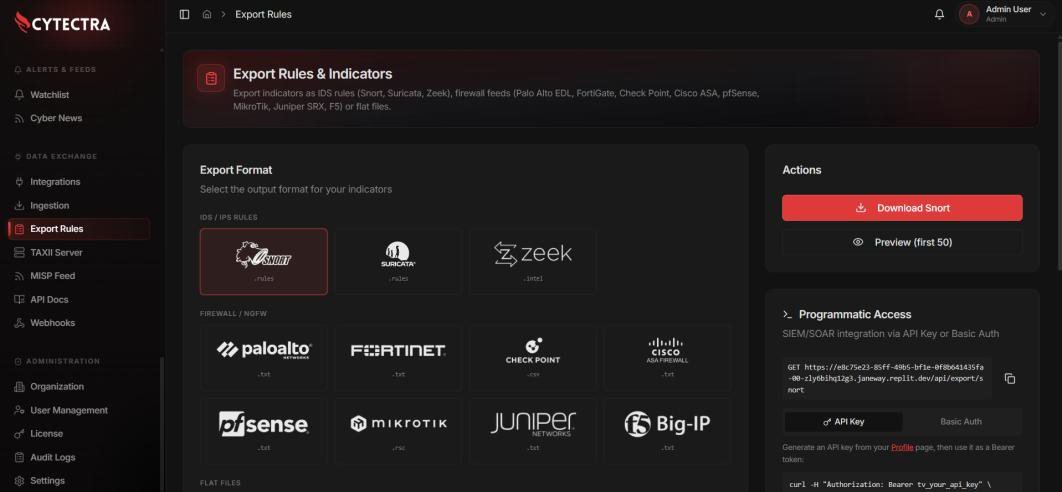
The IDS and Firewall Export modules turn indicators into the detection and blocking formats your devices already speak. Feeds are generated automatically behind stable polling URLs, so the rules stay current without manual work.
Node.js, PostgreSQL, and Nginx already sit inside the official image. The host only needs Docker Engine and Compose.
Enough for one team with a few thousand indicators.
For several active connectors, dark web ingestion, weekly reports, and the AI assistant.
We walk you through the flow from ingestion and correlation to exporting indicators into your devices. The session runs about 45 minutes with our technical team.